Our cases

Clients about us
Custom Digital Platform Development Services
Platform development services for multi-tenant products, marketplaces, and partner portals — not cross-platform apps.
What digital platform development actually means

Digital platform development services from WTT Solutions mean designing and shipping a multi-sided, multi-tenant, API-first product — not a brochure site and not a single-tenant app. Platform development services cover tenancy, identity, data residency, and operator workflows that packaged software will not let you own. This is not cross-platform mobile work and not internal developer-platform or platform-engineering (IDP) work. If you need iOS and Android clients, those consume the platform; they are not the platform. A digital platform development agency engagement starts with isolation models, IdP choice, and region strategy before UI kits. The first one hundred words on this page are the fence: we sell a commercial product plane other companies log into, not a Flutter wrapper and not an internal developer portal.
We build the shared product plane: public and partner APIs, SSO, tenant administration, audit logs, and the operator console your staff actually runs. Custom platform development is how US product teams escape per-seat SaaS and low-code ceilings when the second customer, second region, or second IdP arrives. Native or hybrid apps belong on our Flutter and React Native pages; the API and data plane live in back-end development and front-end development. ERP, billing, and ECM stay on enterprise software development services. Delivery can run as software development outsourcing or a scoped discovery. Digital platform development in this sense is a product you operate for years: versioned APIs, tenant SKUs, and evidence packs your security team can attach to a questionnaire. We would rather spend discovery on isolation and identity than ship a logo switcher that fails the first enterprise RFP. That is the difference between a platform and an app with extra screens — and it is why this URL exists as a hub instead of another generic custom-software landing.
What breaks first when a platform adds its second tenant
Most “platforms” are still single-tenant apps with a logo switcher. The failure shows up in isolation, identity, residency, accessibility, and audits — not in the first demo. US buyers usually feel it when the second tenant, the second IdP, or the first SOC questionnaire arrives. The cards below are the symptoms we design against in discovery so you do not pay for a rewrite six months after launch.
Isolation fails on day two
Pooled databases without row-level and encryption boundaries leak reports, webhooks, and search indexes across customers. Tenant isolation models have to be chosen before the first migration, not after a support ticket. Restore drills and per-tenant keys are part of the same decision — hoping a tenant_id column is enough is how incidents start.
SSO and provisioning stall deals
Enterprise buyers expect OAuth 2.0, OpenID Connect, SAML 2.0, and SCIM. Homegrown login plus CSV imports die in security review and joiner-mover-leaver tickets never close. If your first logo needs Okta and the second needs Azure AD, that is an architecture problem, not a settings page.
Residency and WCAG show up in RFPs
US companies selling into Europe need GDPR lawful basis, DSR workflows, and region pins. Operator and customer UIs that miss WCAG 2.2 AA lose public-sector and healthcare-adjacent deals. Logging and support tools that copy PII into another region are part of the same failure mode.
Monoliths cannot productize
A single deployable without audit logs, secrets hygiene, or control evidence cannot pass SOC 2 Type II. Bolting a marketplace or partner API onto a monolith usually costs more than a platform rewrite. Productizing internal tools without an operate phase leaves you with a demo, not a company other tenants can trust.
Success Stories
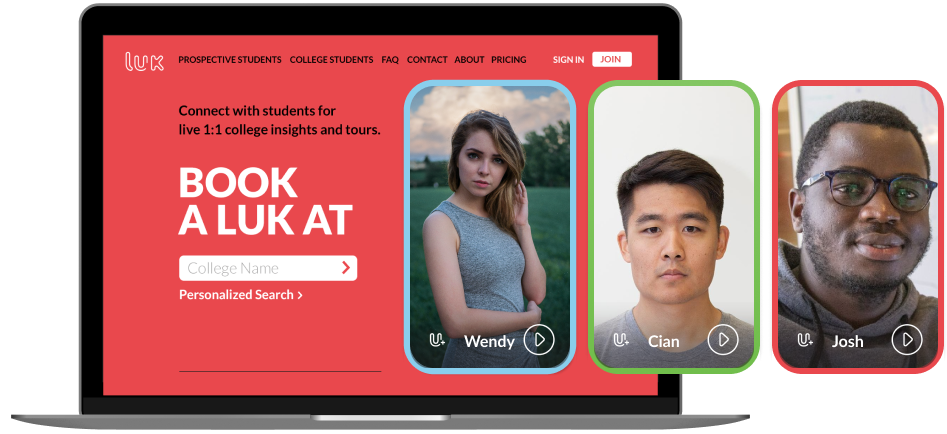
Connect with students for live 1-on-1 college insights and tours
EXPERTISE
Education
TECHNOLOGIES

Platform development services

API and ecosystem
We design public and partner APIs with versioning, deprecation windows, idempotency, and webhook delivery you can operate. A developer portal documents auth, scopes, sandbox tenants, and changelog so integrators do not open tickets for every field. Rate limits and usage plans sit per tenant, not as a global afterthought. Custom digital platform development services treat the API as a product surface equal to the UI — including OpenAPI contracts, example SDKs, and staging that mirrors production tenancy. Partner success depends on this plane: if the API cannot onboard a second integrator without a hotfix, you do not have a platform yet. We also plan breaking-change policy and status pages so ecosystem work does not live in Slack.
API and ecosystem
We design public and partner APIs with versioning, deprecation windows, idempotency, and webhook delivery you can operate. A developer portal documents auth, scopes, sandbox tenants, and changelog so integrators do not open tickets for every field. Rate limits and usage plans sit per tenant, not as a global afterthought. Custom digital platform development services treat the API as a product surface equal to the UI — including OpenAPI contracts, example SDKs, and staging that mirrors production tenancy. Partner success depends on this plane: if the API cannot onboard a second integrator without a hotfix, you do not have a platform yet. We also plan breaking-change policy and status pages so ecosystem work does not live in Slack.

Identity and provisioning
Identity is where B2B platforms win or lose security review. We implement OAuth 2.0 for delegated access, OpenID Connect for user login, SAML 2.0 for enterprise IdPs, and SCIM so joiner, mover, and leaver events stay in the customer's directory. That combination covers SSO, just-in-time accounts, group-to-role maps, and session policies without a custom IdP. We integrate Okta, Auth0, and Azure AD rather than inventing password resets that auditors reject. Tenant-admin invites remain a fallback for customers with no directory, not the default path. Token lifetimes, logout, and break-glass access are documented so questionnaires have answers instead of screenshots.

Multi-tenant cloud
Tenant isolation models — silo, bridge, or pool — are an architecture decision, not a checkbox. Silo gives dedicated compute and data stores for regulated customers. Pool shares infrastructure with strict row-level, schema, and encryption boundaries. Bridge mixes shared services with isolated data planes. We design noisy-neighbor controls, per-tenant encryption keys, and restore drills so one customer’s batch job cannot starve another. Workloads on AWS, Azure, or GCP follow that model instead of a single shared schema with a tenant_id column hoped to be enough. The escape hatch matters: an MVP can start pooled if you can move a whale to silo later without rewriting APIs.

Data plane, GDPR, residency
US-sold platforms still process EU personal data. We map lawful basis, retention, and data-subject request paths under GDPR, and we pin storage and processing to agreed regions so data residency is configurable, not a wiki promise. Exports, deletes, and audit trails are APIs, not tickets. Subprocessors and transfer records are documented so legal can answer enterprise questionnaires without a war room. Healthcare PHI stays on the healthcare hub; this pillar owns the default enterprise bar. Search, logs, and support tooling are in scope — PII that leaks into a US analytics cluster from an EU tenant is still a residency failure.

Experience layer and WCAG 2.2 AA
Operator consoles and customer UIs both ship to WCAG 2.2 AA: keyboard paths, contrast, names and labels, and assistive-tech flows on the screens people actually use. We test critical journeys — invite a tenant admin, connect an IdP, export a report — rather than pasting a badge on a marketing site. Accessibility is part of definition of done so public-sector and healthcare-adjacent buyers are not blocked at procurement. Frontend implementation follows our front-end development practice. Data tables, modals, and SSO timeouts are where admin UIs fail AA; those components are in the same backlog as features, not a separate “a11y sprint.”

Security engineering
Threat models cover tenant boundaries, API abuse, secrets, and admin impersonation. We ship structured audit logs, key rotation, and least-privilege roles before launch, not as a SOC scramble. Penetration testing of APIs, identity, and tenant isolation is a release gate — details live in the FAQ, not a one-line claim. Control evidence maps toward SOC 2 Type II and ISO 27001; dedicated SOC 2 compliance services stay on that page so this hub does not compete for that query. Secrets never live in tickets; impersonation is logged; dependency and access reviews have owners. That is security engineering as product work, not a PDF in a sales folder.
How custom digital platform development works
Discovery through operate — tenancy and identity first, then build, pentest, launch, and run. The sequence is the product: skipping architecture to “start coding” is how second-tenant bugs become incidents. Each step has a named output your CTO can review.
Discovery
We map sides of the marketplace or SaaS, tenancy, IdP inventory, residency, and MVP cuts. You leave with architecture options, a risk list, and a cost band — not a vague deck. Discovery is paid and short so finance can plan without a fake fixed price. If buy-versus-build is still open, we write that note here before anyone staffs a team.
OutputArchitecture options + cost band
Discovery
We map sides of the marketplace or SaaS, tenancy, IdP inventory, residency, and MVP cuts. You leave with architecture options, a risk list, and a cost band — not a vague deck. Discovery is paid and short so finance can plan without a fake fixed price. If buy-versus-build is still open, we write that note here before anyone staffs a team.
OutputArchitecture options + cost band
Architecture
Isolation model, identity (OAuth 2.0 / OIDC / SAML 2.0 / SCIM), data stores, and region pins are decided before feature factories start. This is the step that prevents rewrite six months later. We also name the escape hatch: how a pooled MVP becomes a silo SKU without changing partner APIs. Security gets a diagram they can attach to a questionnaire.
OutputIsolation + IdP diagram
Build
Two-week sprints on API, tenant admin, operator UX, and integrations. You see working software each cycle. Backend and frontend tracks stay explicit so ownership is clear. Definition of done includes WCAG on the journeys we touch and audit logs on admin actions — not a separate hardening phase after demo day.
OutputWorking software each sprint
Pentest
Independent or partner penetration testing covers APIs, identity endpoints, and tenant boundaries. Findings get severity, owners, and a retest before production credentials go live. Cross-tenant reads are in scope on purpose. A marketing-site scan is not this gate.
OutputRetest pack
Launch
Runbooks, SSO with the first design partners, data migration, and observability. We do not call it launched until a second tenant can be provisioned without a hotfix. Support tooling must know which tenant it is touching; otherwise launch is just a deploy.
OutputSecond tenant without hotfix
Operate
SLOs, audit-log retention, dependency and control evidence, and a backlog for the next isolation or region. Platforms that stop here rot; we plan the operate phase in discovery. Annual cost is typically a fraction of build — pretending operate is free is how questionnaires fail a year later.
OutputSLO + control evidence
Custom digital platform vs packaged SaaS, low-code, or “just an app”
Digital platform development services exist because packaged SaaS, low-code, and single-tenant apps fail different tests. Custom wins when other companies log in, partners hit your APIs, or isolation, SSO, residency, or WCAG 2.2 AA show up in the RFP. Then scope a discovery if custom still wins.
- Advantage
- Limitation or compromise
- Criterion not met
What custom digital platform development costs in the US
Ranges for planning conversations, not quotes. Discovery de-risks tenancy and identity so you are not buying a fake fixed price. An MVP in the $50,000–$150,000 band is a first production tenant, one SSO path, core APIs, and a pentest gate. Full multi-tenant SaaS and marketplace work typically sits at $150,000–$400,000+ when silo or bridge isolation, several IdPs with SCIM, region pins, and an operate phase are in scope. Clinical SaaS pricing lives on SaaS development for healthcare professionals. Annual operate is usually 15–25% of build; exclude it and the platform rots. Numbers below are US commercial platforms — not LMS SKUs and not ERP.
Discovery
Scoped engagement
3–4 weeks
- Tenancy and identity options
- Residency and GDPR map
- MVP cut and risk register
- Architecture + cost band
- No obligation to build with us
MVP platform
$50k – $150k
3–6 months
- First production tenancy model
- SSO for one IdP path
- Core APIs + operator console
- WCAG-minded critical journeys
- Launch + pentest gate
Multi-tenant / marketplace
$150k – $400k+
6–14 months
- Silo/bridge/pool isolation
- OAuth, OIDC, SAML, SCIM
- Region pins and DSR APIs
- Partner APIs + developer portal
- Operate phase and control evidence
Client reviews: platform development company
INDUSTRY RECOGNITION


Luklabs
Acting CEO
The team is smart, creative, nice, calm, and professional, and they are problem solvers.
WTT Solutions paid attention to details. Most of their first iterations were very close to our intended designs. Consequentially, we didn’t have to do a ton of revisions in the QA phase.
I greatly enjoyed working with them.


Types of platforms we build
This hub covers product platforms — not LMS productization and not ERP. SaaS platform development here means generic multi-tenant commercial software in any industry: tenant admin, billing hooks, and APIs other companies automate against. Clinical multi-tenant products go to healthcare SaaS so HIPAA stays on that cluster. Marketplace platform development has no separate landing, so two-sided markets live here. Customer and partner portals are in scope when they authenticate into your data plane, not when they are a CMS theme. DXP-like content-and-data products are in scope when you will own the codebase. Industry operations platforms are in scope when you are productizing internal tools for customers or partners. Use the cards to pick a shape in discovery; we will send industry-specific compliance to the spoke that already owns it.

SaaS platform development
Multi-tenant product with billing, tenant admin, and APIs. For clinical SaaS see SaaS development for healthcare professionals — this card is the generic product pattern, including saas platform development services for non-clinical commercial SKUs.

Marketplace platform development
B2B or B2C two-sided markets: listings, matching, payments, dispute and operator tools. Mobile storefronts are clients; the marketplace is the platform. Liquidity features and KYC sit on this spine, not on a separate “app project.”

Customer and partner portals
Authenticated portals on top of your data plane — not a CMS theme. SSO into the customer’s IdP, role-based objects, and APIs partners can automate. If the portal is only for your own staff, say so in discovery; productization is a different cut.

Content and data platforms
DXP-like content plus operational data: catalog, workflow, and distribution APIs. We do not resell a boxed DXP; we build the product you will own, with tenancy and identity as first-class rather than a CMS plugin.

Industry operations platforms
Line-of-business platforms that productize internal tools for customers or partners. One mention: enterprise software development services for ERP-class systems belongs on the enterprise hub, not here. If you need billing, ECM, or call-center suites, follow that link.
Industries that buy digital platforms
01

Healthcare
SOC 2 and GDPR sit on this pillar. HIPAA, FHIR, and clinical workflow live on the custom healthcare software hub. AI in hospitals is a spoke: healthcare AI platform development. Digital health productization stays on its own URL so this hub does not steal that phrase.
02

EdTech
Learning products, not this URL. LMS and instructional platforms: EdTech software development. If you need a commercial multi-tenant product that happens to serve schools, we still split LMS standards onto EdTech and keep tenancy here.
03

Fintech and ops
Multi-tenant ledgers, partner APIs, and audit-heavy operator consoles. Isolation and evidence matter more than a payment widget. We will not pretend a checkout form is a platform.
04

MarTech
CDP-like and campaign ops platforms. Industry-modified work: MarTech software development. Consent, server-side tagging, and tenant-scoped audiences belong in that hub’s language; isolation still follows this architecture.
05

HR tech
Workforce platforms with SSO and SCIM. Product detail: HR software development. Employee data rights still need GDPR and residency on the shared plane described above.
06

Retail and marketplaces
Seller portals, catalog, and order platforms. Mobile apps remain clients of the platform, not a substitute for tenancy. If you only need a storefront app, start on mobile — not here.

Platform architecture: multi-tenancy, identity, data residency
Architecture copy is the opposite of protocol-name stuffing. Tenancy, identity, observability, CI/CD, and accessibility are how a platform survives the second tenant and the first audit. We document each as an explicit workstream so US buyers can map it to their security questionnaire. The cards below are the default plane we ship; industry spokes add HIPAA or LMS standards without moving those queries onto this URL. If a control is not listed, it is probably a spoke — or it is not a platform concern yet.

Tenancy models
Silo, bridge, or pool with encryption and restore drills per tenant.

Identity plane
OAuth 2.0, OIDC, SAML 2.0, SCIM against Okta, Auth0, or Azure AD.

Observability
Per-tenant traces, audit logs, and alerting that security can read.

CI/CD and environments
Preview tenants, migration gates, and secrets that never sit in tickets.

Accessibility
WCAG 2.2 AA on operator and customer journeys, not only the homepage.

Residency controls
Region pins, DSR APIs, and subprocessors you can name in a DPA.

API product
Versioning, webhooks, developer portal, and per-tenant rate limits.

Control evidence
Logs and access reviews that map toward SOC 2 Type II and ISO 27001.


Technology stack for digital platform development
 OpenAI
 Google Gemini
 Anthropic Claude
 LangChain
 LlamaIndex
 Perplexity API
 RAG / Pinecone / Qdrant


 PostgreSQL
 MySQL
 MongoDB
 Redis
 Docker
 Kubernetes
 Terraform
 GitHub Actions


Here’s how you can get in touch
Digital platform development — frequently asked questions
What are digital platform development services?
This work is not the same as building a cross-platform mobile app. If you need iOS and Android clients, that is application delivery — see our Flutter app development and React Native practices — and those clients consume the platform rather than replacing it. It is also not platform engineering in the internal-developer-platform sense: we do not sell IDPs, paved roads, or DevOps platform teams. Software platform development here means a commercial or partner-facing system your customers log into.
A typical engagement starts with tenancy and identity, not with a UI kit. We decide silo versus pool versus bridge isolation, which IdP you already run (Okta, Auth0, Azure AD), and which data must stay in US or EU regions before we write the first service. That is why buyers comparing a digital platform development agency should evaluate architecture discipline, not slide-deck feature lists. If you already have ERP or billing systems, we integrate rather than replace them — and we point enterprise application work to our enterprise development practice so this hub stays focused on product platforms.
How much does custom digital platform development cost in the US?
The upper band appears when you need silo or bridge isolation for regulated tenants, several IdPs with SCIM, partner developer portals, region pins, and an operate phase with control evidence. Marketplace liquidity features, complex matching, and payments add scope the same way extra IdPs do. Hosting, observability, and support after launch are typically 15–25% of build per year; pretending they are free is how platforms rot.
Published ranges on the internet that start at $20,000 usually describe a single-tenant app or a low-code prototype. Those numbers are useful as a floor for experiments, not as a quote for a product other companies will log into. We give a written band after discovery so finance can plan without a fake fixed price. Clinical products should budget on the healthcare SaaS page; this pillar’s numbers are for generic multi-tenant commercial platforms sold into the US, including US companies with EU customers. Ask for the band in writing after discovery; we will not invent a $20k “platform” that is actually a single-tenant prototype.
Custom digital platform vs buying SaaS or low-code — when to build?
The five-year cost often reverses the first-year sticker. Packaged SaaS looks cheap until SCIM, a private region, or a partner API is a premium SKU — or unavailable. Low-code looks fast until you need audit logs a SOC 2 assessor will accept or a noisy-neighbor problem you cannot debug. A single-tenant app looks done until the second customer requires a rewrite. Custom costs more upfront and then converts variable vendor rent into infrastructure you operate.
We still tell clients to buy when buy is honest. During discovery we run a short build-versus-buy note so you are not paying us to recreate a commodity CRM. If the gap is only a mobile client, do not commission a platform; use our mobile practices. If the gap is ERP, go to enterprise software development services. If the gap is tenancy plus identity plus APIs you will own, this is the page. The comparison table above is the same conversation in one view for your CTO and finance lead.
How do you implement SSO and user provisioning?
In practice we integrate Okta, Auth0, and Azure AD (Entra ID) as the common IdPs, plus customer-hosted SAML where needed. We map IdP groups to application roles per tenant, enforce session policies, and log admin impersonation. Just-in-time provisioning can stand up a first login; SCIM keeps the directory true after that. Tenant admins invite users only when the customer has no IdP, which is increasingly rare in B2B.
Security review fails when an app invents its own identity store as the source of truth. We keep the customer directory authoritative, store only the claims we must, and document token lifetimes, logout, and break-glass. That package is what enterprise buyers mean by “SSO.” If you only needed a consumer social login, you would not be on this page. Identity work is sequenced in architecture before feature factories so you do not retrofit SAML after the first logo on the website. If your first three customers share one IdP, we still design for the fourth who will not.
What accessibility standard do you build to?
Why this page cares: public-sector, education-adjacent, and healthcare-adjacent buyers will ask. A platform that only customers with a mouse can operate will fail procurement even if the API is excellent. We test with keyboard and screen-reader spot checks on critical flows and we log defects like any other severity. VPAT language, when a buyer needs it, is produced from the same evidence, not invented in sales.
Accessibility is not a visual theme. It affects component libraries, data tables, modal dialogs in tenant admin, and timeout handling on SSO. Our front-end development practice owns the implementation patterns; this hub owns the requirement that both operator and customer surfaces meet AA. If a product is internal-only and the buyer waives AA in writing, we still keep keyboard paths because support staff will thank you. We do not claim AAA or a full legal certification unless that is a scoped audit. Accessibility on a digital platform is procurement hygiene for US public-sector and healthcare-adjacent buyers, not a design flourish.
Do you build marketplace and SaaS platforms or only internal portals?
SaaS platform development on this page means generic commercial multi-tenant software. Clinical multi-tenant products are built under SaaS development for healthcare professionals so HIPAA and clinical workflow stay on the healthcare cluster. Learning platforms stay on EdTech. That split is how we avoid cannibalizing our own URLs while still naming the type of platform you want.
If you only need a native app that talks to someone else’s backend, you are not buying platform work. If you need other businesses to log in, extend via API, and remain isolated, you are. We would rather decline a portal restyle than ship a fake platform. The types section on this page is the inventory; pick the shape in discovery and we will tell you which spoke, if any, should own industry-specific compliance. Portals, SaaS, and marketplaces share one identity and tenancy spine; they do not share a single landing page for every industry modifier. If you only need an internal dashboard, say so — we will not upsell a marketplace you will not operate.
How do you handle security compliance (SOC 2 Type II, ISO 27001)?
What is included in platform development services?
Identity and provisioning are first-class, not a plugin. We implement OAuth 2.0, OpenID Connect, SAML 2.0, and SCIM so enterprise SSO and joiner-mover-leaver flows survive security review. The data plane includes GDPR-aligned lawful basis, data-subject request paths, and configurable data residency. The experience layer targets WCAG 2.2 AA on both operator and customer UIs. Security engineering covers threat modeling, secrets, audit logs, and a penetration-test gate before production credentials go live.
What we do not bundle into this page: LMS or e-learning productization (that is EdTech), clinical healthcare SaaS, or SOC 2 as a standalone compliance engagement. You still get control evidence that maps toward SOC 2 Type II and ISO 27001, and we link SOC 2 compliance services when you need that program. Delivery can be a dedicated team or software development outsourcing depending on who owns the backlog. The output is a platform you operate — not a pile of tickets against a vendor you cannot inspect. If you need extra seats under your PM instead of vendor-owned delivery, that is IT staff augmentation, not a different architecture.
How long does it take to build a digital platform (MVP vs multi-tenant SaaS)?
A production multi-tenant SaaS with SCIM, more than one isolation mode, region pins, partner APIs, and WCAG-backed operator journeys usually takes six to fourteen months to a stable release. Marketplaces add matching, payments, and dispute tooling on top of the same spine. We work in two-week sprints with working software each cycle so you are not waiting for a big-bang launch. The milestone we care about is “second tenant provisions without a hotfix,” not “we deployed once.”
Timelines slip for predictable reasons: undefined sides of the market, a late requirement to support SAML plus OIDC, a residency promise made in sales that engineering never designed, or treating accessibility as a last-week audit. We put those decisions in discovery so the build calendar is honest. Mobile clients, if needed, can trail the API; they should not gate the platform MVP. If you already have a monolith, modernization (see the FAQ below) is a parallel track with its own cutover plan rather than a hidden extra month. Calendar honesty is part of platform development services: we would rather quote six months than pretend isolation is a weekend flag.
What is multi-tenant architecture and which isolation model should we use?
Which model you should use is not a branding choice. If a healthcare-adjacent or public-sector buyer will ask for dedicated encryption keys and restore drills, start silo or bridge for those SKUs even if the SMB tier is pooled. If you are early and every tenant is similar, pool with encryption and excellent observability is usually the honest MVP — provided you can migrate a whale to silo later without a rewrite. We design that escape hatch in discovery: same APIs, different deploy topology.
Failures we see in the wild: a single shared schema with tenant_id and no query tests; search indexes that leak; webhooks that fire the wrong tenant’s data; backups that cannot restore one customer. Isolation is also operational: deploy cadence, feature flags, and support tooling must know which tenant they are touching. Platform development services that skip this conversation are just app development with extra steps. We make the model explicit in architecture docs your security team can attach to a questionnaire.
How do you handle GDPR and data residency on a US-sold platform?
Technically that means region-aware data stores, careful replication (you cannot silently copy EU personal data to a US analytics cluster), and backups that respect the same pins. Search, logs, and support tooling are part of the data plane; putting PII in a shared logging product in another region is a classic own-goal. We treat DSR deadlines as product SLAs: export and delete jobs have owners and evidence.
This pillar does not try to rank for HIPAA. Protected health information and BAA workflows belong on the custom healthcare software hub. Here the default enterprise bar is GDPR plus residency plus auditability, which is what most US B2B platforms actually get asked. If a tenant needs a dedicated EU silo, that is an isolation SKU we plan in discovery rather than a weekend configuration flag. Buyers should assume residency is an architecture decision with a cost, not a checkbox on a marketing site. Put residency in the contract and in the architecture the same week, or sales will sell a region you cannot operate.
Can you modernize a legacy monolith into a platform?
Typical pattern: introduce an API gateway and canonical identity (OAuth 2.0 / OIDC / SAML) in front, extract the data that cannot leak, and run dual-write or CDC until the new store is source of truth for that context. Search, jobs, and file storage are where monoliths hide cross-tenant bugs; we test those early. You should budget discovery specifically for the as-is architecture — undocumented stored procedures are cheaper to find in week one than in month four.
We will also tell you when modernization is the wrong spend. If the monolith is a single-tenant tool for your own staff, productizing it may be less valuable than buying SaaS or building a thin portal. If the business goal is a mobile app, do not start with a platform rewrite. If the goal is to sell the same workflows to other companies, modernization is exactly this practice. Delivery can sit under outsourcing when you want vendor-owned execution, or alongside your team when they keep the monolith alive during the strangler. Either way, the second tenant must land on the new plane — that is the definition of done for modernization.
What tech stack do you use for digital platform development?
We add observability (traces, metrics, structured audit logs) per tenant, CI/CD with preview environments, and secrets management that never lives in chat. Search, webhooks, and file pipelines are designed so they cannot leak across tenants. None of this is a religion; if your team is already deep in a stack we can operate, we use it, provided isolation and identity are not compromised for convenience.
What we will not do is pick a stack because it is trendy in a blog. Platform development company evaluations should ask how the stack maps to tenancy, IdP, and region pins — not whether we used the same language as last year’s conference. Mobile clients, when required, follow Flutter or React Native on their own pages so this hub stays on the shared plane. The Tools section on this page lists the families we actually deploy; discovery names the concrete services for your account. A platform development company that cannot explain tenancy in the stack conversation is selling staff, not architecture. Ask us to name the IdP, the isolation model, and the region pins in the same sentence as the framework.
