Our cases

Clients about us
MarTech Software Development Services
A MarTech development company for US product and healthcare teams that need custom MarTech developers — not a HubSpot reseller, not a CMP vendor, and not a jobs board.
What custom MarTech software development actually means

Custom MarTech software development means you own the data plane: identity, consent, suppression, and activation — not a rented SKU that meters every event. Our martech development services design first-party collection and server-side GTM so ads and analytics fire only after a lawful basis, and so healthcare campaigns never leak PHI into a client-side pixel. HIPAA restrictions on pixels and trackers, and the OCR bulletin on tracking technologies, decide what may fire; a BAA with advertising platforms is required before any equivalent identifier is shared. We are a MarTech development company for product teams and healthcare marketers who already outgrew packaged MAP or CDP pricing, cookie-based identity, or a tag manager nobody can audit. This is not a consulting slide deck and not an agency media retainers page. If you need a multi-tenant commercial product that is not a marketing-stack SKU, that work lives on platform development. Clinical systems, EHR, and care workflows belong on the healthcare software hub. Marketing mobile clients consume this plane; they are built under mobile app development.
The architecture thesis is simple: first-party data plus server-side collection, with consent timestamps that automation cannot bypass. Enterprise builds can map access, logging, and change control to SOC 2 Type II evidence in the product. We wire HubSpot, Salesforce, Braze, Segment, GA4, Meta, and Google Ads as systems of record or activation — not as the product you are stuck renting forever. Feature inventories for a MarTech SaaS you sell live in our notes on building MarTech SaaS products; commercial delivery stays on this URL. Encyclopedia intent — what marketing technology is — belongs on what is marketing technology. AI features inside a stack (scoring, recommendations, assistants) are scoped on AI services when data quality allows, not bolted on as theater. You leave discovery with a lawful-basis map, an identity store, and a measurement plan your security and legal teams can read — then we build.
What breaks when cookies, consent, and healthcare pixels collide
Most “MarTech stacks” are a tag manager, a MAP seat, and a hope that identity survives Safari. US buyers feel it when cookies drop, consent breaks paid media, packaged CDPs invoice per event, or a healthcare pixel sees PHI. Industry ranges below are labels, not fake precision.
Cookie deprecation loses the person
Third-party cookies and probabilistic IDs fail in Safari, Firefox, and tightening Chrome defaults. Journeys stall because the same person looks like three anonymous hits. First-party collection and a durable identity key have to be designed, not hoped for in a pixel.
Where consent rules limit what marketing data you can use
Banners collect a choice, then GTM still fires everything. Google Consent Mode v2 and IAB TCF 2.2 only work if tags read the signal. Denied purposes must suppress pixels — otherwise legal has a banner and marketing has a leak.
Packaged MAP/CDP lock-in
Per-event and per-contact pricing looks cheap until a successful program multiplies cost. You cannot change the identity model or add a healthcare-safe path without a vendor SKU. Custom MarTech application development exists so the event bus is yours.
HIPAA and OCR tracker risk
Client-side Meta or Google tags on appointment or symptom pages can see PHI. The OCR bulletin on tracking technologies treats those pixels as a disclosure risk. Healthcare marketing needs BAA-aware pipelines and no health data in ad tags — not a “we anonymized the URL” comment.

MarTech development services we actually ship

Consent-gated multi-channel activation
We build named journeys, not a generic “marketing automation” box. A healthcare activation product we engineered confirms a booking, then runs a 72-hour SMS, 48-hour email, and 4-hour voice pass for high-risk contacts — one-tap confirm, cancel that offers the next slot. On this pillar that pattern is a preference and suppression fabric: TCPA timestamps, CAN-SPAM unsubscribe, quiet hours, and channel fallback encoded so automation cannot fire without a record. Healthcare variant: no PHI in Meta or Google pixels; identifiers stay first-party. Clinic reminder products and scheduling SKUs are not this URL — those belong on patient engagement software. What you get here is the consent-correct orchestration layer US and healthcare marketers can operate without inventing a new CMP vendor relationship for every channel.
Consent-gated multi-channel activation
We build named journeys, not a generic “marketing automation” box. A healthcare activation product we engineered confirms a booking, then runs a 72-hour SMS, 48-hour email, and 4-hour voice pass for high-risk contacts — one-tap confirm, cancel that offers the next slot. On this pillar that pattern is a preference and suppression fabric: TCPA timestamps, CAN-SPAM unsubscribe, quiet hours, and channel fallback encoded so automation cannot fire without a record. Healthcare variant: no PHI in Meta or Google pixels; identifiers stay first-party. Clinic reminder products and scheduling SKUs are not this URL — those belong on patient engagement software. What you get here is the consent-correct orchestration layer US and healthcare marketers can operate without inventing a new CMP vendor relationship for every channel.

Live system-of-record write-back
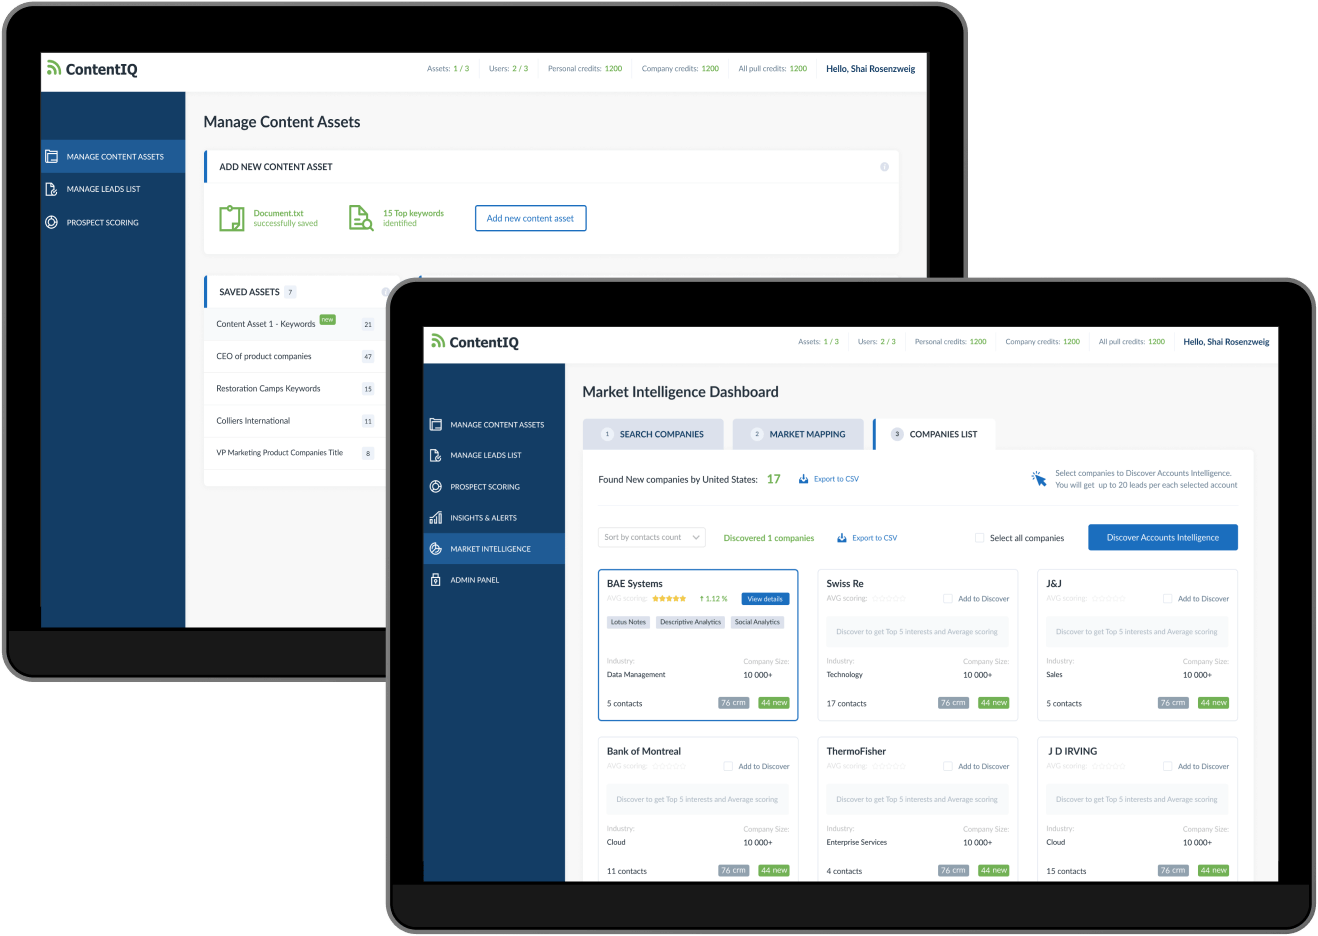
No overnight CSV and no stale audience cache. We read live availability, audiences, and preferences from HubSpot, Salesforce, Braze, a warehouse, or an EHR — then write confirmations, unsubscribes, and slot changes back through rate-limit-aware APIs. Identity is resolved before ad IDs. Server-side GTM keeps events first-party so measurement does not depend on a browser tag that Safari will strip. Healthcare: a BAA with advertising platforms is required before any equivalent identifier is shared, which is how we read the OCR bulletin on tracking technologies — not as a blog citation, as a release gate. This is MarTech integration services and marketing CRM / MAP overlay work. It is not clinic CRM: patient-relationship systems for care teams stay on the healthcare CRM page linked from the industries section.

Hire MarTech developers for a live stack
Dedicated MarTech developers join when you already have a MAP or CDP in production and it is leaking pixels, ignoring consent, or too expensive to retarget. The pod takes over tagging, identity, and journey code under your backlog — the secondary intent behind “martech developers” as a service, never as jobs or salary content. Engagement can run as IT staff augmentation when your PM owns the board, or as a scoped project when we own delivery. Conversational front doors are one sentence here: assistants and chat UIs go to AI chatbot development services. Clinical voice or scheduling products are not this URL. You hire people who have shipped consent-gated journeys and live write-back, not a bench of generic JavaScript seats.
How MarTech platform development works
Five delivery steps, not Scrum theater. Each step has a named output your counsel and growth lead can review. Skipping the lawful-basis map is how PHI lands in a pixel.
Lawful-basis and BAA map
We list which events may leave the brand, which purposes they serve, and whether a BAA is required before voice, SMS, or ads. OCR tracking risk is called out if a pixel would see PHI. Deep HIPAA program work stays on HIPAA compliance consulting; this step is engineering scope.
OutputEvent + BAA decision log
Lawful-basis and BAA map
We list which events may leave the brand, which purposes they serve, and whether a BAA is required before voice, SMS, or ads. OCR tracking risk is called out if a pixel would see PHI. Deep HIPAA program work stays on HIPAA compliance consulting; this step is engineering scope.
OutputEvent + BAA decision log
Identity and consent store
We persist who the person is, consent timestamps, purpose, channel, and suppression. Automation cannot send without that record. Healthcare capture may verify identity before a write — the MarTech analog of checking a name before a booking — without turning this page into a clinical product.
OutputConsent + identity schema
Live read/write to the system of record
Slots, audiences, and preferences are read live. Writes are idempotent. No overnight CSV. Server-side GTM and first-party collection are designed here so GA4, ads, and the warehouse see the same consented event.
OutputSoR API + sGTM plan
Channel orchestration with quiet hours
Named steps: confirm, remind, recover, backfill. High-risk segments may get voice; others SMS or email. TCPA and CAN-SPAM are enforced in code — timestamps, unsub, and quiet hours — not in a policy PDF.
OutputJourney graph + suppressions
PHI-safe measurement and backfill
Confirmations and unsubs write back. Cancelled or exhausted audience members can be replaced without client-side health pixels. Tag QA plus Consent Mode v2 and TCF 2.2 signaling is a release gate, not a slide.
OutputQA gate + waitlist analog
Custom MarTech development vs packaged HubSpot, Salesforce, Braze, or Segment
Packaged stacks win speed when the SKU fits. Custom MarTech software development wins when you need HIPAA/BAA feasibility, pixel control, or event economics at volume. Then scope a discovery if custom still wins.
- Advantage
- Limitation or compromise
- Criterion not met
What custom MarTech software development costs
Ranges for planning, not quotes. Discovery is typically $15k–$40k and de-risks consent, identity, and BAA questions before a fake fixed price. MVP MarTech platform development sits at $40k–$90k over 3–4 months. Growth work is $90k–$180k over 5–8 months. Enterprise is custom and 6+ months when multi-tenant productization, HIPAA-safe measurement, server-side GTM plus warehouse, and SOC 2 Type II evidence are in scope — those constraints raise the band; we say so up front. Hosting and operate are extra. Ask for a written band after discovery.
MVP stack
$40k – $90k
3–4 months
- Consent + identity store
- One live SoR write-back path
- sGTM-ready first-party events
- One named journey (confirm / remind)
- Tag QA gate
Growth
$90k – $180k
5–8 months
- Multi-channel orchestration
- Warehouse + MAP/CRM overlays
- Consent Mode v2 / TCF 2.2
- Suppression and backfill
- Healthcare-safe measurement path
Enterprise
Custom
6+ months
- Multi-tenant MarTech product
- HIPAA / BAA event map
- sGTM + warehouse + SOC 2 evidence
- Dedicated MarTech developers
- Operate phase and control logs
Client reviews: MarTech development company in production
INDUSTRY RECOGNITION


Pitch59
Product Manager
The team at WTT Solutions is responsive, communicative, and a pleasure to work with. The website is functioning much better thanks to their impeccable attention to detail. They have great personalities and they’re well run. They’re responsible and communicate well. They’re incredibly involved and they care.


Industries we serve
Healthcare is the home for HIPAA pixel limits, the OCR bulletin on tracking technologies, and BAAs with advertising platforms. Other industries get consent and measurement — we do not stuff clinical terms into agency cards. MarTech SaaS vendors, digital agencies, ecommerce, and financial services buy the same data-plane pattern with different risk.
Healthcare and life sciences
HIPAA limits what pixels and trackers may see. The OCR bulletin on tracking technologies treats client-side tags on health pages as a disclosure risk. We keep PHI out of ad tags, require a BAA with advertising platforms before equivalent identifiers move, and implement HIPAA-compliant IT controls in the pipeline. Clinic CRM is a different URL: one outbound sentence — patient-relationship / clinic CRM is healthcare CRM software development.
MarTech SaaS vendors
Product companies that sell MAP, CDP-like, or analytics SKUs hire us to build the product — tenancy-aware event APIs, consent objects, and sGTM connectors your customers will operate. Feature essays stay on the blog; commercial MarTech software development services stay here.
Digital agencies and AdTech
Agencies get consent-correct tagging, first-party measurement, and server-side collection — not HIPAA copy pasted into an agency card. DSP/SSP-adjacent work is in scope when we can name the integration; otherwise we say so in discovery.
Ecommerce and retail
First-party audiences, suppression, and consented checkout events without third-party cookie theater. Server-side GTM keeps purchase signals durable when browsers drop client tags.
Financial services
We mention fintech only where a real measurement or consent build exists. If your case is a generic bank website, we will not invent a MarTech case study. Ask in discovery; we stay honest.
Types of MarTech solutions we build
01

Multi-touch confirmation and reminders
Consent-correct confirm / remind / recover sequences across SMS, email, and voice with quiet hours and one-tap actions — not a blast calendar.
02

System-of-record live sync
CRM, CDP, MAP, or EHR write-back that reads live and writes idempotently. Marketing CRM overlays — not a clinic system of record.
03

First-party and server-side measurement
sGTM, first-party events, and no PHI in ad tags. Analytics and attribution you can defend in a security review.
04

Suppression and audience backfill
Re-eligibility, unsub, and waitlist-style replacement when a contact cancels or exhausts — without recrawling health pages in a pixel.
05

Always-on capture with human escalation
Conversational capture that hands to a human. One line: chat products live on AI chatbot development services — no medical-receptionist H2 here.

MarTech architecture we actually ship
Identity, first-party collection, server-side GTM, and consent signaling are the default plane. CAN-SPAM and TCPA live in the preference center. SOC 2 Type II is control mapping in the product — program work is SOC 2 compliance services. AI only where data quality allows.

Identity resolution
First-party keys before ad IDs. Dedup across MAP, CRM, and warehouse.

First-party data collection
Events you collect on your domain — not a third-party cookie bet.

Server-side GTM
sGTM so GA4 and ads see consented hits browsers no longer send.

Consent Mode v2 + TCF 2.2
Signals tags must honor. Denied purposes do not fire pixels.

CAN-SPAM / TCPA preferences
Unsub, timestamps, and quiet hours in the preference center — in code.

SOC 2 Type II mapping
Access, logging, and change evidence in the product we build.

GDPR + CCPA/CPRA
Lawful basis, DSR paths, and US state privacy in the same store.

Scoped AI
Forecasts, recs, assistants only on clean consented data — via AI services.


MarTech stack we work with: CDP, CRM, server-side GTM, consent
 OpenAI
 Google Gemini
 Anthropic Claude
 LangChain
 LlamaIndex
 Perplexity API
 RAG / Pinecone / Qdrant


 PostgreSQL
 MySQL
 MongoDB
 Redis
 Docker
 Kubernetes
 Terraform
 GitHub Actions


Here’s how you can get in touch
MarTech development services — questions we answer
What is MarTech software development?
People searching “what is martech” usually want a definition of the category. That encyclopedia intent belongs on our article what is marketing technology. This page is the commercial hub: MarTech software development services for teams that already know they need software, not a glossary. We still define the work so buyers are not sold a banner and a hope. A typical build includes an identity key that survives cookie loss, a consent store that automation must read, server-side GTM for first-party hits, and journeys that cannot send without TCPA or CAN-SPAM records where those laws apply.
What we do not treat as MarTech on this URL: clinical EHR, care-team CRM, or patient portals. Those are healthcare products. Multi-tenant commercial platforms that are not a marketing SKU belong on platform development. If you only need a brochure site, you are in the wrong place. If you need to own measurement and activation under US privacy and healthcare advertising constraints, this is MarTech software development as we sell it — and the rest of this FAQ is how we implement it.
Why hire a MarTech development company instead of HubSpot, Salesforce, Braze, or Segment?
Custom does not mean “rewrite HubSpot.” It often means an overlay: you keep the MAP or CRM as system of record and own identity, consent, sGTM, and the journeys that packaged templates cannot gate. IP ownership matters if you are a vendor selling a MarTech product, or if you need to change the identity model without a SKU veto. Packaged still wins a two-week launch for a simple nurture. We say that in the comparison table so this is not a religious argument.
The five-year cost often reverses the first invoice. A CDP that charges per event looks cheap until the program works. A healthcare-safe path that is “coming on the enterprise plan” is not a path. We run a short build-versus-buy note in discovery. If buy is honest, buy. If you need a MarTech development company because counsel, security, or unit economics already rejected the SKU, this page is the brief — not an agency pitch to migrate you for billable hours.
How long does MarTech platform development take?
Growth work that adds multi-channel orchestration, warehouse sync, Consent Mode v2 and TCF 2.2 as a hard gate, and audience backfill usually takes five to eight months. Enterprise productization (you sell the MarTech SKU), HIPAA-safe measurement, and SOC 2 evidence in the operate phase usually take six months or more to a stable release. We work in two-week cycles with working software each sprint. The milestone we care about is “a consented event writes back and a denied purpose does not fire a pixel,” not “we published a container.”
Timelines slip for predictable reasons: legal has not decided lawful basis, sales promised a Meta pixel on a symptoms page, the CRM cannot accept writes, or accessibility and tag QA are left for the week before launch. We put those decisions in the lawful-basis and BAA map so the calendar is honest. Mobile clients can trail the API. If you already have a broken GTM, remediation is a parallel track with its own cutover, not a hidden extra month. Calendar honesty is part of the service: we would rather quote five months than pretend consent is a weekend flag.
Which platforms and APIs do you integrate?
Healthcare adds a constraint, not a different connector list: if an equivalent identifier would leave the brand toward an ad platform, we ask whether a BAA exists and whether the payload can contain PHI. Often the honest answer is “no client-side pixel; measure server-side with a minimized event.” EHR write-back for activation (slot taken, reminder sent) is in scope as a system of record, not as a clinical module. Identity is resolved before ad IDs so you are not stitching emails in a spreadsheet after the campaign.
We will not pretend every DSP or SSP is a standard SKU. Adtech-adjacent work is in scope when we can name the API and the case; otherwise it is discovery. CMS and social publishing hooks are supported when they share the same consent store. If your stack is something we have not shipped, we say so and estimate the adapter. The point of custom MarTech application development is that the integration contract is yours — versioned, logged, and testable — not a Zap that dies when a field is renamed.
How do email and SMS stay compliant with CAN-SPAM and TCPA?
Implementation looks like code, not a policy wiki. Email templates include the required identity and unsub. SMS and voice paths check TCPA consent and quiet hours. High-risk segments may get voice; others get SMS or email — that is orchestration, still gated. We log the decision so a complaint has a trail. We are not your counsel; if you need a legal opinion on “express written consent” for a specific campaign, bring an attorney. We implement the controls they describe.
Healthcare adds a second gate: the message body and the landing page must not push PHI into an ad pixel when someone taps a reminder. That is the OCR tracking issue, not CAN-SPAM. The two problems get confused in Slack; we keep them separate in the event map. If your ESP or SMS vendor cannot honor suppression in near real time, we say so in discovery — a custom fabric cannot fix a vendor that ignores unsub. This FAQ is why the preference-center chip exists on the features list.
What are server-side GTM and first-party data in your builds?
In our builds, sGTM is designed in the live read/write step, not bolted on after a leak. Events are named, purpose-tagged, and dropped when consent is denied. Healthcare events are stripped of PHI before any ad destination. Identity is a first-party key; ad IDs are attached only when allowed. We still use client-side tags where they are lawful and sufficient; we do not religiously move everything server-side to inflate scope.
What sGTM is not: a way to ignore consent (“the server can still ping Meta”). If the purpose is denied, the server does not send. It is also not a CMP. You still need Consent Mode v2 and, for EU ads vendors, TCF 2.2 signals. First-party data is also not a license to hoard. Retention and DSR still apply under GDPR and CCPA/CPRA. If a vendor asks you to paste a health-page pixel “just for matching,” that is the opposite of this architecture.
What is the difference between MarTech and AdTech in your work?
People search “what is adtech and martech” because the categories blurred. We keep them separate so this page does not pretend to be an ad network. If you need a custom bidder or exchange, that is a different scope and we will say whether we have shipped it. If you need consented audiences and server-side conversion APIs into existing ad platforms, that is this page. Healthcare makes the split sharper: AdTech pixels on health pages are the OCR problem; MarTech is how you measure without that pixel.
Agencies often buy both. Their card on this page is consent and measurement, not a promise that we will operate campaigns. Product companies that sell into marketing departments are MarTech SaaS vendors on the industries list. If your question is really “should we hire an agency,” that is not our H1 — we are a development company.
How do email and SMS outreach stay compliant?
What MarTech development services do you offer?
Around those shapes we implement analytics and attribution, marketing CRM / MAP overlays (not clinic CRM), CMS or social publishing hooks, adtech-adjacent connectors when we can name the case, and consent plus tag orchestration (Consent Mode v2, TCF 2.2). Conversational capture is one line plus a link to our chatbot practice — we do not rank this URL for chatbot queries. Stack audits and roadmap advice exist as a discovery line, not as a “MarTech consulting” H1. Feature checklists for a product you sell are on the SaaS blog post; the build is here.
Engagement is a scoped project, a vendor-managed build, or seats under your PM. Integrations we see most: Salesforce, HubSpot, Braze, Segment, GA4, Meta, Google Ads, and sGTM. Healthcare adds a BAA question before any ad identifier moves. You do not get blockchain, IoT, or VR theater. You get a written event map, a consent store, and software your counsel can review. If the SKU already fits and legal is happy, we will tell you to stay on packaged software.
How much does custom MarTech software development cost?
What an MVP usually includes: a consent and identity store, one live write-back path to a system of record, sGTM-ready first-party events, one named journey (confirm or remind), and a tag QA gate. It does not include every ad destination, every state privacy edge, or a SOC 2 audit. Growth adds suppression, backfill, and more channels. Enterprise adds the operate phase and control logs your assessor will sample. Annual operate and hosting are typically a fraction of build; pretending they are free is how stacks rot.
Published “MarTech project” numbers under $20,000 usually describe a tag install or a HubSpot template, not custom MarTech software development. We will not invent that floor to win a form fill. Ask for a written band after discovery so finance can plan without a fake fixed price. If you only need seats, staff-augmentation rates are a different conversation on that page — this FAQ is project cost for a stack you will own.
Can I hire MarTech developers to extend my team?
If your PM owns prioritization and you want seats, that engagement model is IT staff augmentation. If you want vendor-managed delivery — we own milestones, QA, and release — use software development outsourcing. Same engineers, different governance. We do not put “martech developers” in the staff-augmentation title; that phrase lives here so the two URLs do not compete. You still get domain people: tagging, identity, TCPA/CAN-SPAM in code, and HIPAA-aware measurement.
What you should not hire this pod for: media buying, HubSpot admin only, or a clinical scheduling product. Conversational UIs go to the chatbot page. We shortlist people who can explain Consent Mode v2 and a BAA question in the same interview. Ramp is weeks, not a six-month recruiting cycle. If you need a full rebuild rather than an extension, skip seats and run the five-step delivery on this page as a project.
How do you implement GDPR, CCPA/CPRA, Google Consent Mode v2, and IAB TCF 2.2?
In a build, the CMP or first-party preference center writes purpose, timestamp, and region into a store journeys and sGTM must read. Tags are configured to wait. Denied analytics or ads purposes do not fire client-side pixels and do not get reconstructed “for quality” in a shadowy second container. DSRs fan out to MAP, CRM, warehouse, and logs on a deadline. We are not your law firm: counsel picks lawful basis and TCF vendor lists; we implement the gates and keep evidence that a send or a hit had a record.
US-only teams still meet Consent Mode v2 if they use Google tags, and they still meet CCPA/CPRA if they have California residents. EU traffic adds TCF and GDPR. We do not claim “GDPR certified software.” We claim the stack can enforce the signal. Optional split of EU vs US is a configuration in the same store, not a second product. If your current GTM fires everything and the banner is theater, remediation starts here — before another campaign spend.
How do you build MarTech for healthcare (HIPAA, OCR tracking bulletin, BAAs)?
A Business Associate Agreement is a contract, not a badge. We execute BAAs where we are a business associate. Ad platforms are a separate question your counsel and the vendor must answer; we implement the “do not send until BAA exists” gate. Program-level HIPAA — policies, risk analysis, workforce training — lives on HIPAA compliance consulting and IT operations on HIPAA-compliant IT services. Patient-relationship / clinic CRM is healthcare CRM software development — that is the one sentence we use that phrase, so this URL does not steal it.
We do not claim “HIPAA certified software.” We claim PHI-safe measurement and a documented event map. If sales wants a pixel on a pre-visit form, we will refuse that configuration and propose a first-party confirmation flow instead. That is how a MarTech development company should behave on YMYL-adjacent marketing.
Do you support SOC 2 Type II for a MarTech product we sell?
SOC 2 Type II is an attestation over a period of operating effectiveness. We do not sell the audit and we do not pretend a codebase is “SOC 2 certified” on launch day. We implement the technical hooks your assessor will look for and partner with your GRC owner on scope. Dedicated readiness, policies, and vendor reviews live on SOC 2 compliance services so this pillar does not rank for that service keyword. If sales already promised Type II by a date, tell us in discovery so the operate phase is in the plan.
Healthcare buyers may ask HIPAA and SOC 2 in the same RFP. HIPAA marketing constraints stay on this URL; the attestation program stays on the SOC 2 page. You get both conversations without keyword cannibalization. If you only need a HubSpot portal for an internal team, you do not need Type II on a custom stack — buy the SKU. If you sell a MarTech product into hospitals, tell us in discovery so logging and access reviews match how those buyers write questionnaires.
How do you handle consent and privacy rules in MarTech builds?
Why WTT Solutions for US and healthcare MarTech builds?
You can hire MarTech developers as a pod or run a full project. You can start from get started with a discovery that produces a lawful-basis map instead of a mood-board. We will send clinical work to the healthcare hub, generic multi-tenant work to platform development, and chatbot UIs to the AI chatbot page so we do not cannibalize our own URLs. That discipline is how you know the content is for ranking the right query, not stuffing every phrase onto one landing.
We are not your law firm, not a CMP vendor, and not a HubSpot agency. If packaged software fits, we will say so. If you need a MarTech development company that will refuse a PHI-in-pixel configuration, this is the brief. The answers on this page are the support-article version of that offer — use them with counsel, then staff the build. Bring the event list you think you need; we will mark which ones may leave the brand.
